Detect threats before they escalate
Argus analyzes behavior patterns, monitors activity in real time, and provides context-rich alerts to stop threats at the source.
- Category
- DETECTION
- Deployment
- SaaS / Self-hosted
- Telemetry
- Real-time
- Integrations
- 96+
[ Overview ]
A streaming detection engine evaluates every event against behavioral baselines, MITRE ATT&CK techniques, and curated threat intel — surfacing only the signals that matter.
Live Threat Intelligence Correlation
Argus continuously ingests global threat feeds and matches them against activity in your environment. This ensures known threats are flagged immediately, so your team is never caught off guard.
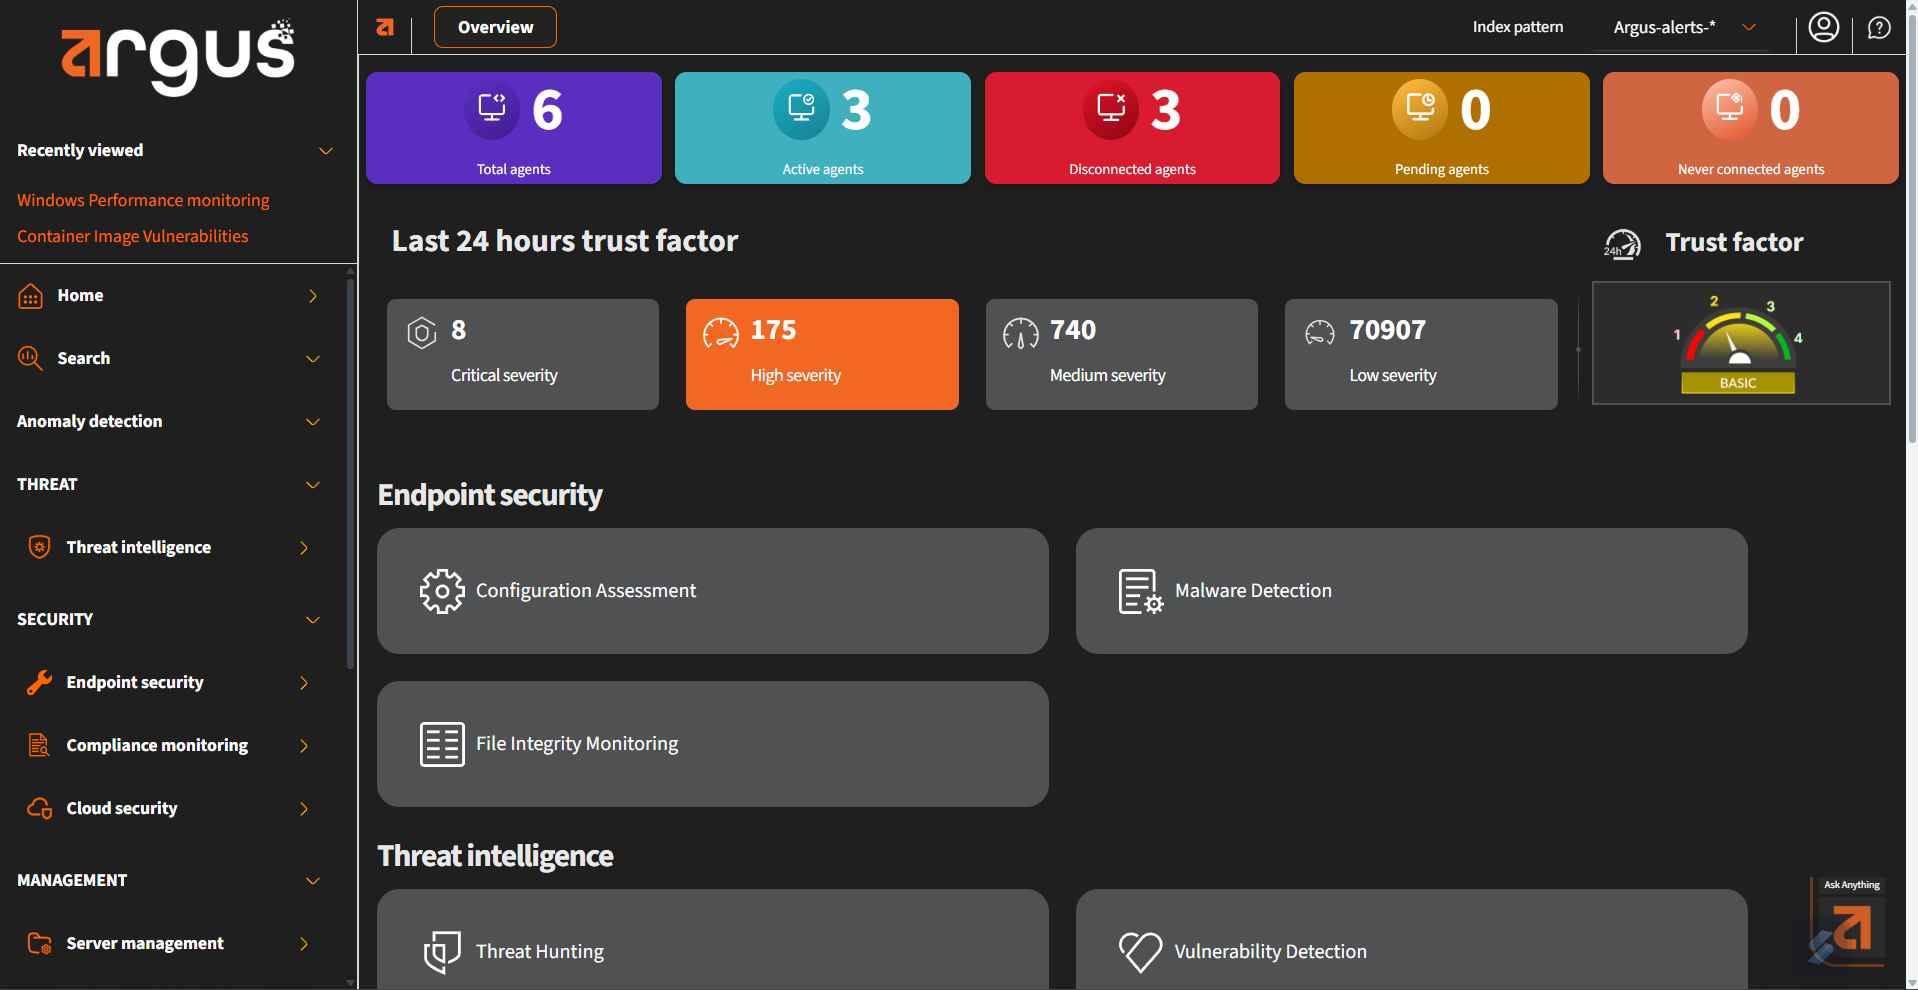
AI-Driven Anomaly Detection
Our machine learning models are trained to recognize unusual behaviors based on your organization's baseline. From unauthorized access attempts to lateral movement, Argus detects what doesn't belong and alerts you in real time.
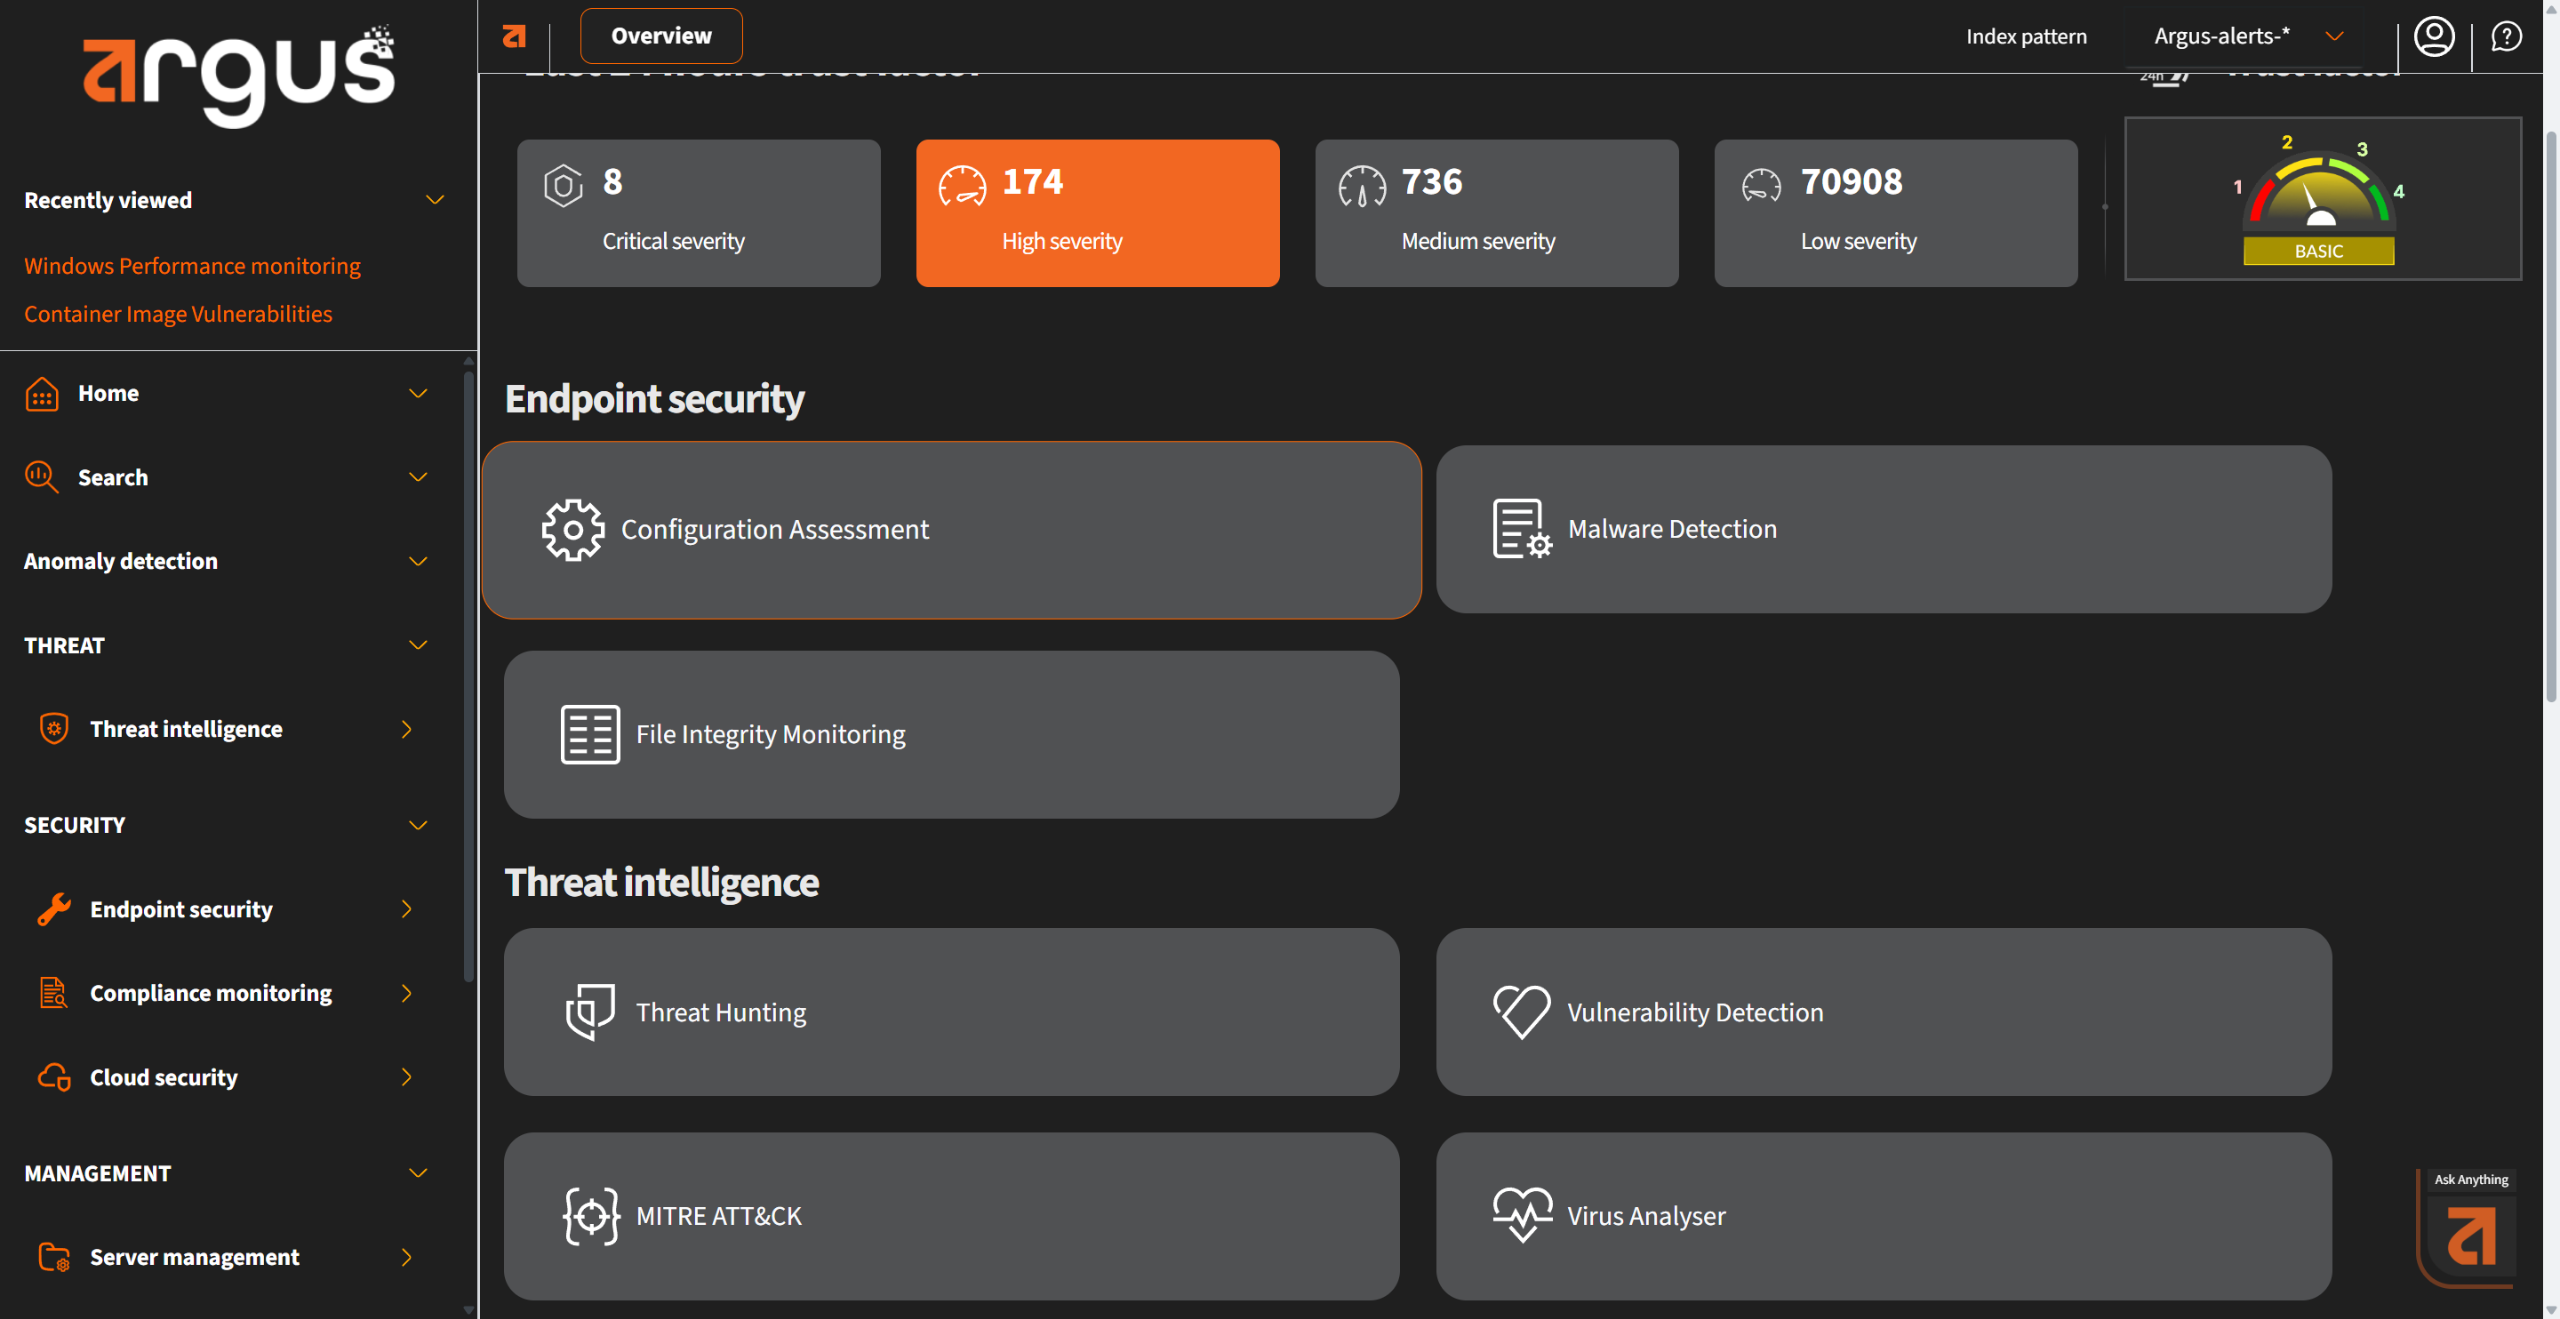
In-Depth Context for Every Alert
Each alert includes detailed context about the affected asset, user behavior, timeline, and potential impact. This reduces noise, prevents alert fatigue, and accelerates triage and investigation.
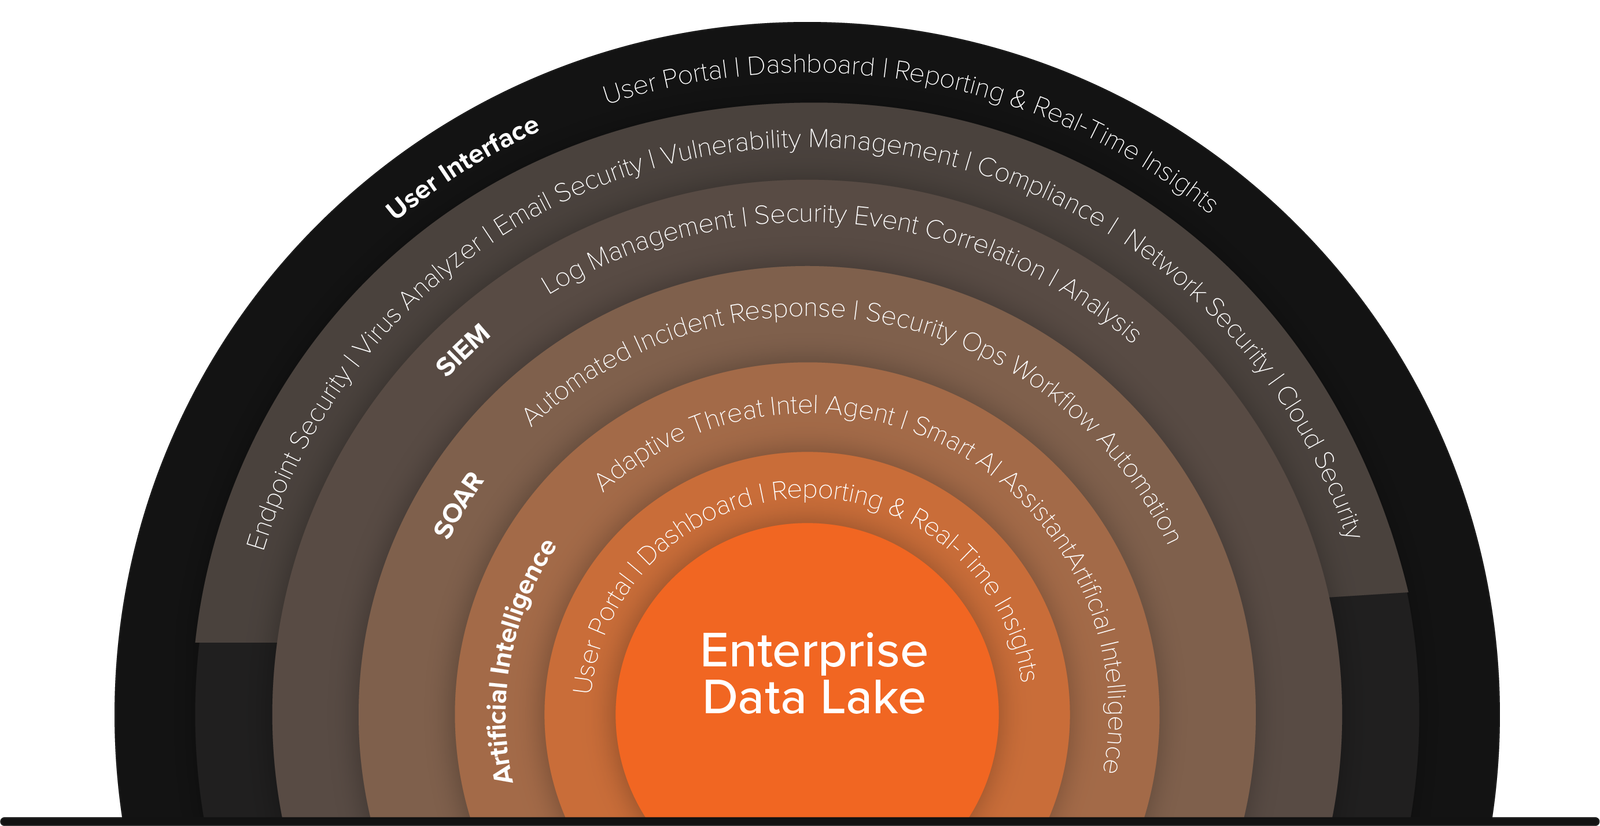
Continuous Monitoring Across Your Environment
From cloud workloads to on-premise servers, Argus keeps a real-time watch over all your assets. It analyzes user behavior, network traffic, file activity, and more to create a live threat picture that updates by the second.
Smart AI Assistant for Investigation and Insights
Argus includes a built-in AI assistant that helps security teams interpret alerts and suggest next steps. It identifies the root cause of events, links them to known attack patterns, and provides actionable guidance.
Eliminate Alert Overload
Instead of flooding your SOC with irrelevant alerts, Argus prioritizes incidents based on severity and business impact. This helps your team focus on the threats that truly matter, reducing response time and stress.
Why Choose Argus for Real-Time Threat Detection
Real-time visibility, context-rich alerts, and AI-assisted investigation in one converged platform.
Stay a step ahead with detection that never sleeps
Talk to an engineer to see how Argus transforms your detection and response capabilities.
[ Related capabilities ]
[ INTEGRATIONS ]
Third-Party Tool Integrations
Argus connects natively to CrowdStrike, SentinelOne, Microsoft, Okta, and 95+ other tools — orchestrating detection, investigation, and response across them from a single platform.
[ EXPOSURE ]
Vulnerability Management
Argus continuously scans your environment, simulates real-world attacks, and guides your team with actionable remediation to eliminate risks before they're exploited.
[ INTELLIGENCE ]
AI-Powered Analytics
Argus analyzes behaviors across users and systems to identify risky activity, predict threats in real time, and support your team with actionable insights.
Ready when you are
See Argus in your environment
Talk to an engineer for a 30-minute working session and see how Argus converges detection, response, and exposure management into a single platform.