Stay One Step Ahead of Ransomware Attacks
Argus instantly spots suspicious file behavior, contains impacted systems, and restores them to a safe state — so your business stays uninterrupted.
- Category
- DEFENSE
- Deployment
- SaaS / Self-hosted
- Telemetry
- Real-time
- Integrations
- 96+
[ Overview ]
From initial access to lateral movement to mass-encryption, Argus identifies the early-stage tradecraft of modern ransomware crews and triggers automated containment.
Early Detection Before Encryption Begins
Argus uses behavioral analysis and file activity monitoring to detect ransomware-like movements such as bulk encryption or unauthorized access. It flags threats before damage begins.
Smart Recovery with Built-In Workflows
Argus enables automatic rollback and asset recovery using safe restore points. Your systems can bounce back without relying on disconnected backup systems or manual cleanup.
Rapid Containment to Stop Lateral Spread
Once Argus confirms a threat, it immediately contains the affected device or user. This ensures that malicious software cannot move across the network or access shared resources.
Single-Flow Response Mechanisms
Ransomware protection is directly tied to Argus's automated response engine. Detection and mitigation are not just fast — they are part of a single workflow.
Detailed Forensic Logging
All detected incidents are captured with context, showing origin, timeline, affected files, and resolution path. This is useful for investigation and reporting.
Zero Dependency on Manual Intervention
Everything from detection to recovery can operate autonomously, ensuring protection even during off-hours or in understaffed environments.
Why Choose Argus for Ransomware Protection
Argus does not just notify you about ransomware risks. It handles them completely — from the first signal to full recovery.
Stop ransomware before it stops your business
Talk to an engineer to experience end-to-end ransomware defense with Argus.
[ Related capabilities ]
[ INTEGRATIONS ]
Third-Party Tool Integrations
Argus connects natively to CrowdStrike, SentinelOne, Microsoft, Okta, and 95+ other tools — orchestrating detection, investigation, and response across them from a single platform.
[ DETECTION ]
Real-Time Threat Detection
Argus analyzes behavior patterns, monitors activity in real time, and provides context-rich alerts to stop threats at the source.
[ EXPOSURE ]
Vulnerability Management
Argus continuously scans your environment, simulates real-world attacks, and guides your team with actionable remediation to eliminate risks before they're exploited.
Ready when you are
See Argus in your environment
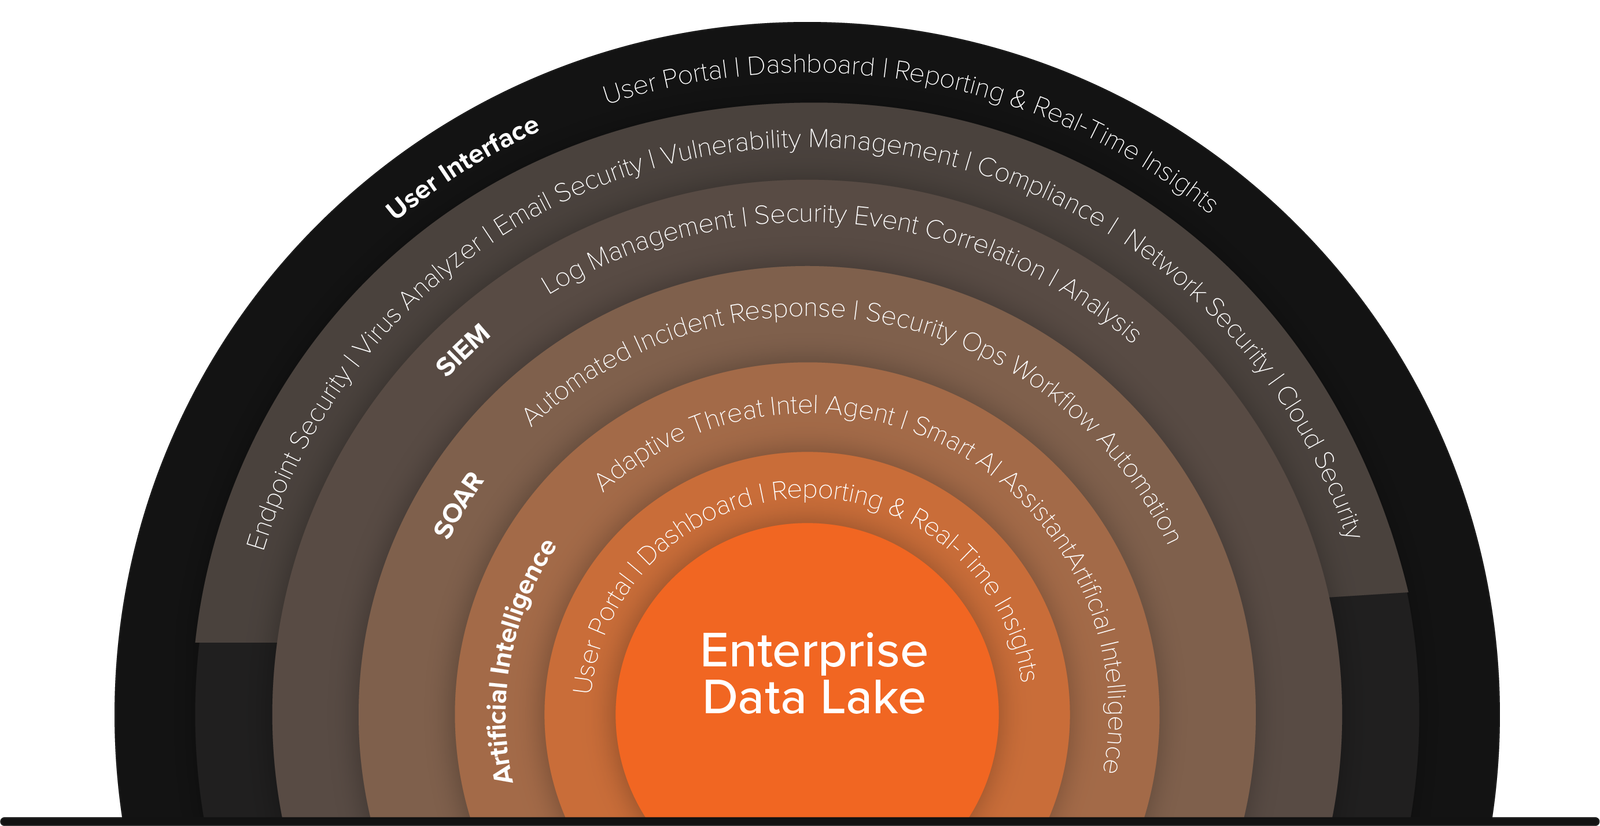
Talk to an engineer for a 30-minute working session and see how Argus converges detection, response, and exposure management into a single platform.