A modern SIEM that scales with your stack
High-throughput log ingestion, intelligent correlation, and seamless integration with the SIEMs your team already uses.
- Category
- TELEMETRY
- Deployment
- SaaS / Self-hosted
- Telemetry
- Real-time
- Integrations
- 96+
[ Overview ]
A modern SIEM core that ingests, parses, and correlates logs at petabyte scale — without the storage bills or tuning overhead of legacy platforms.
Real-Time Log Collection and Analysis
Argus continuously ingests data from your servers, endpoints, applications, and cloud environments. It normalizes and analyzes logs in real time, helping you stay on top of security incidents as they happen.
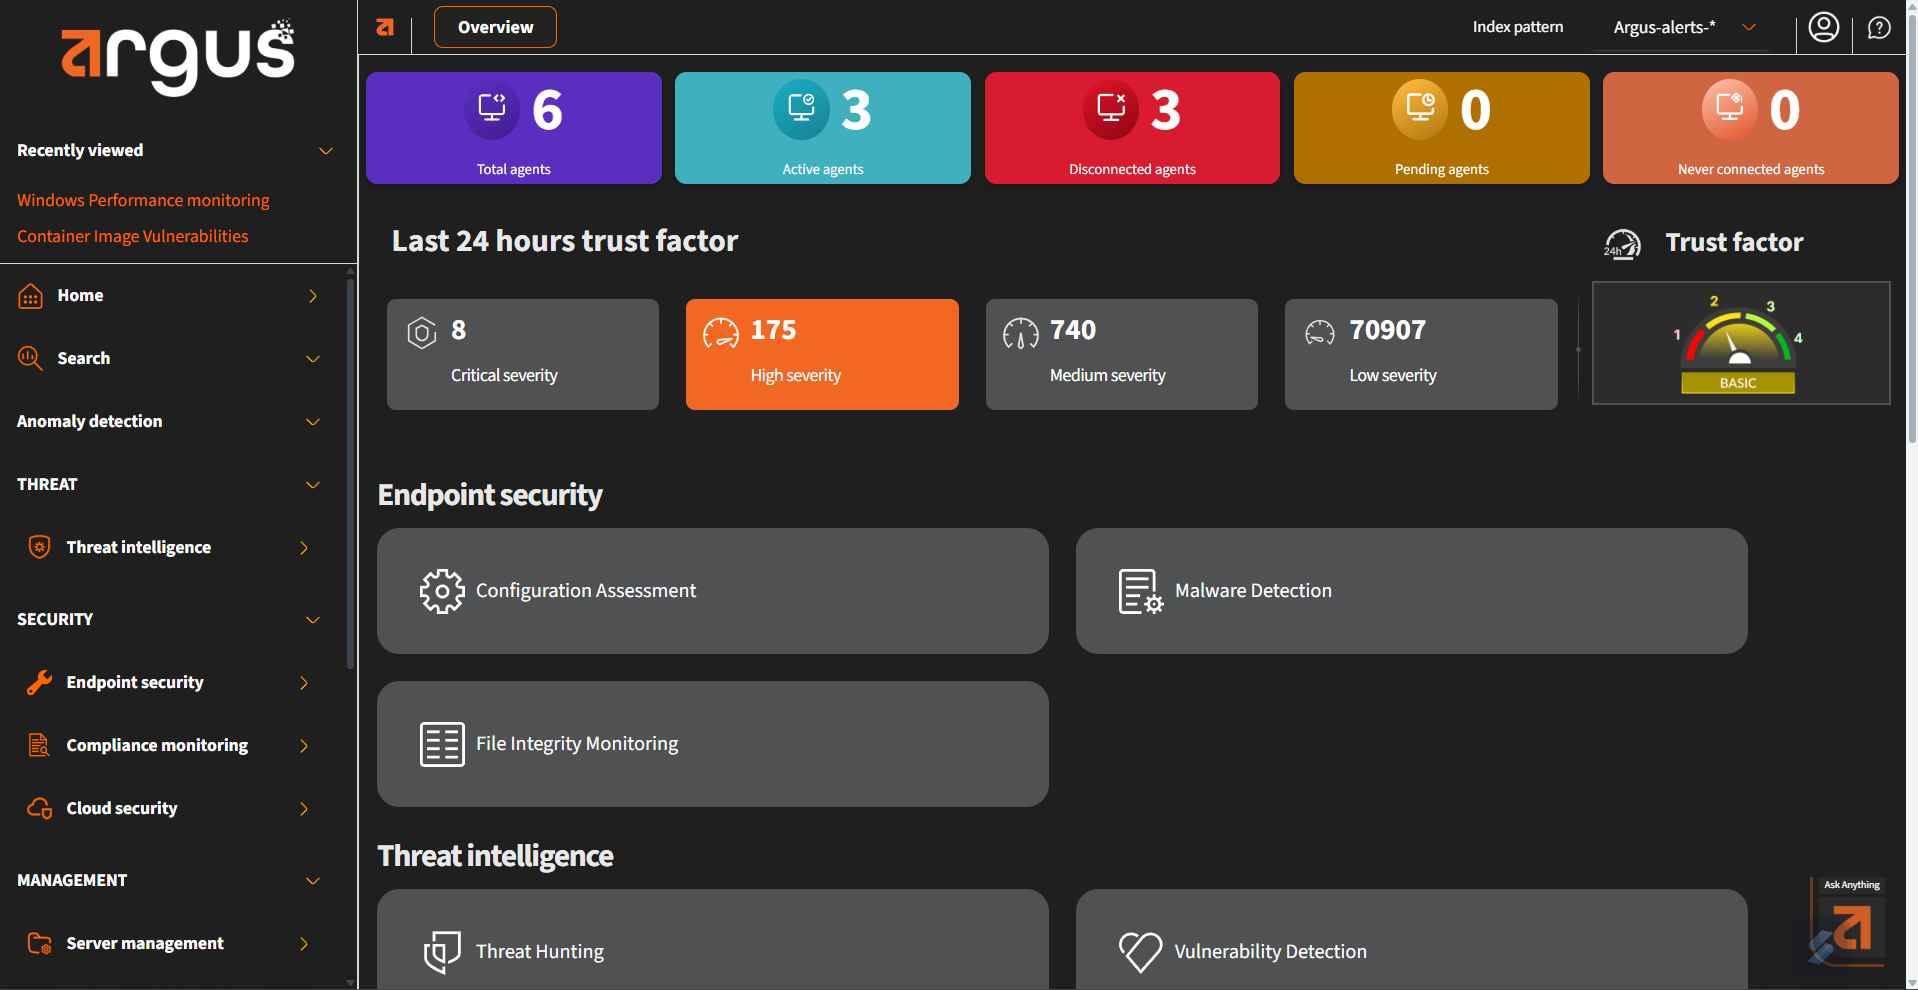
Smart Correlation and Alerting
The built-in SIEM uses intelligent rules and behavioral baselines to detect anomalies and known attack patterns. Alerts are actionable, noise-free, and prioritized based on severity.
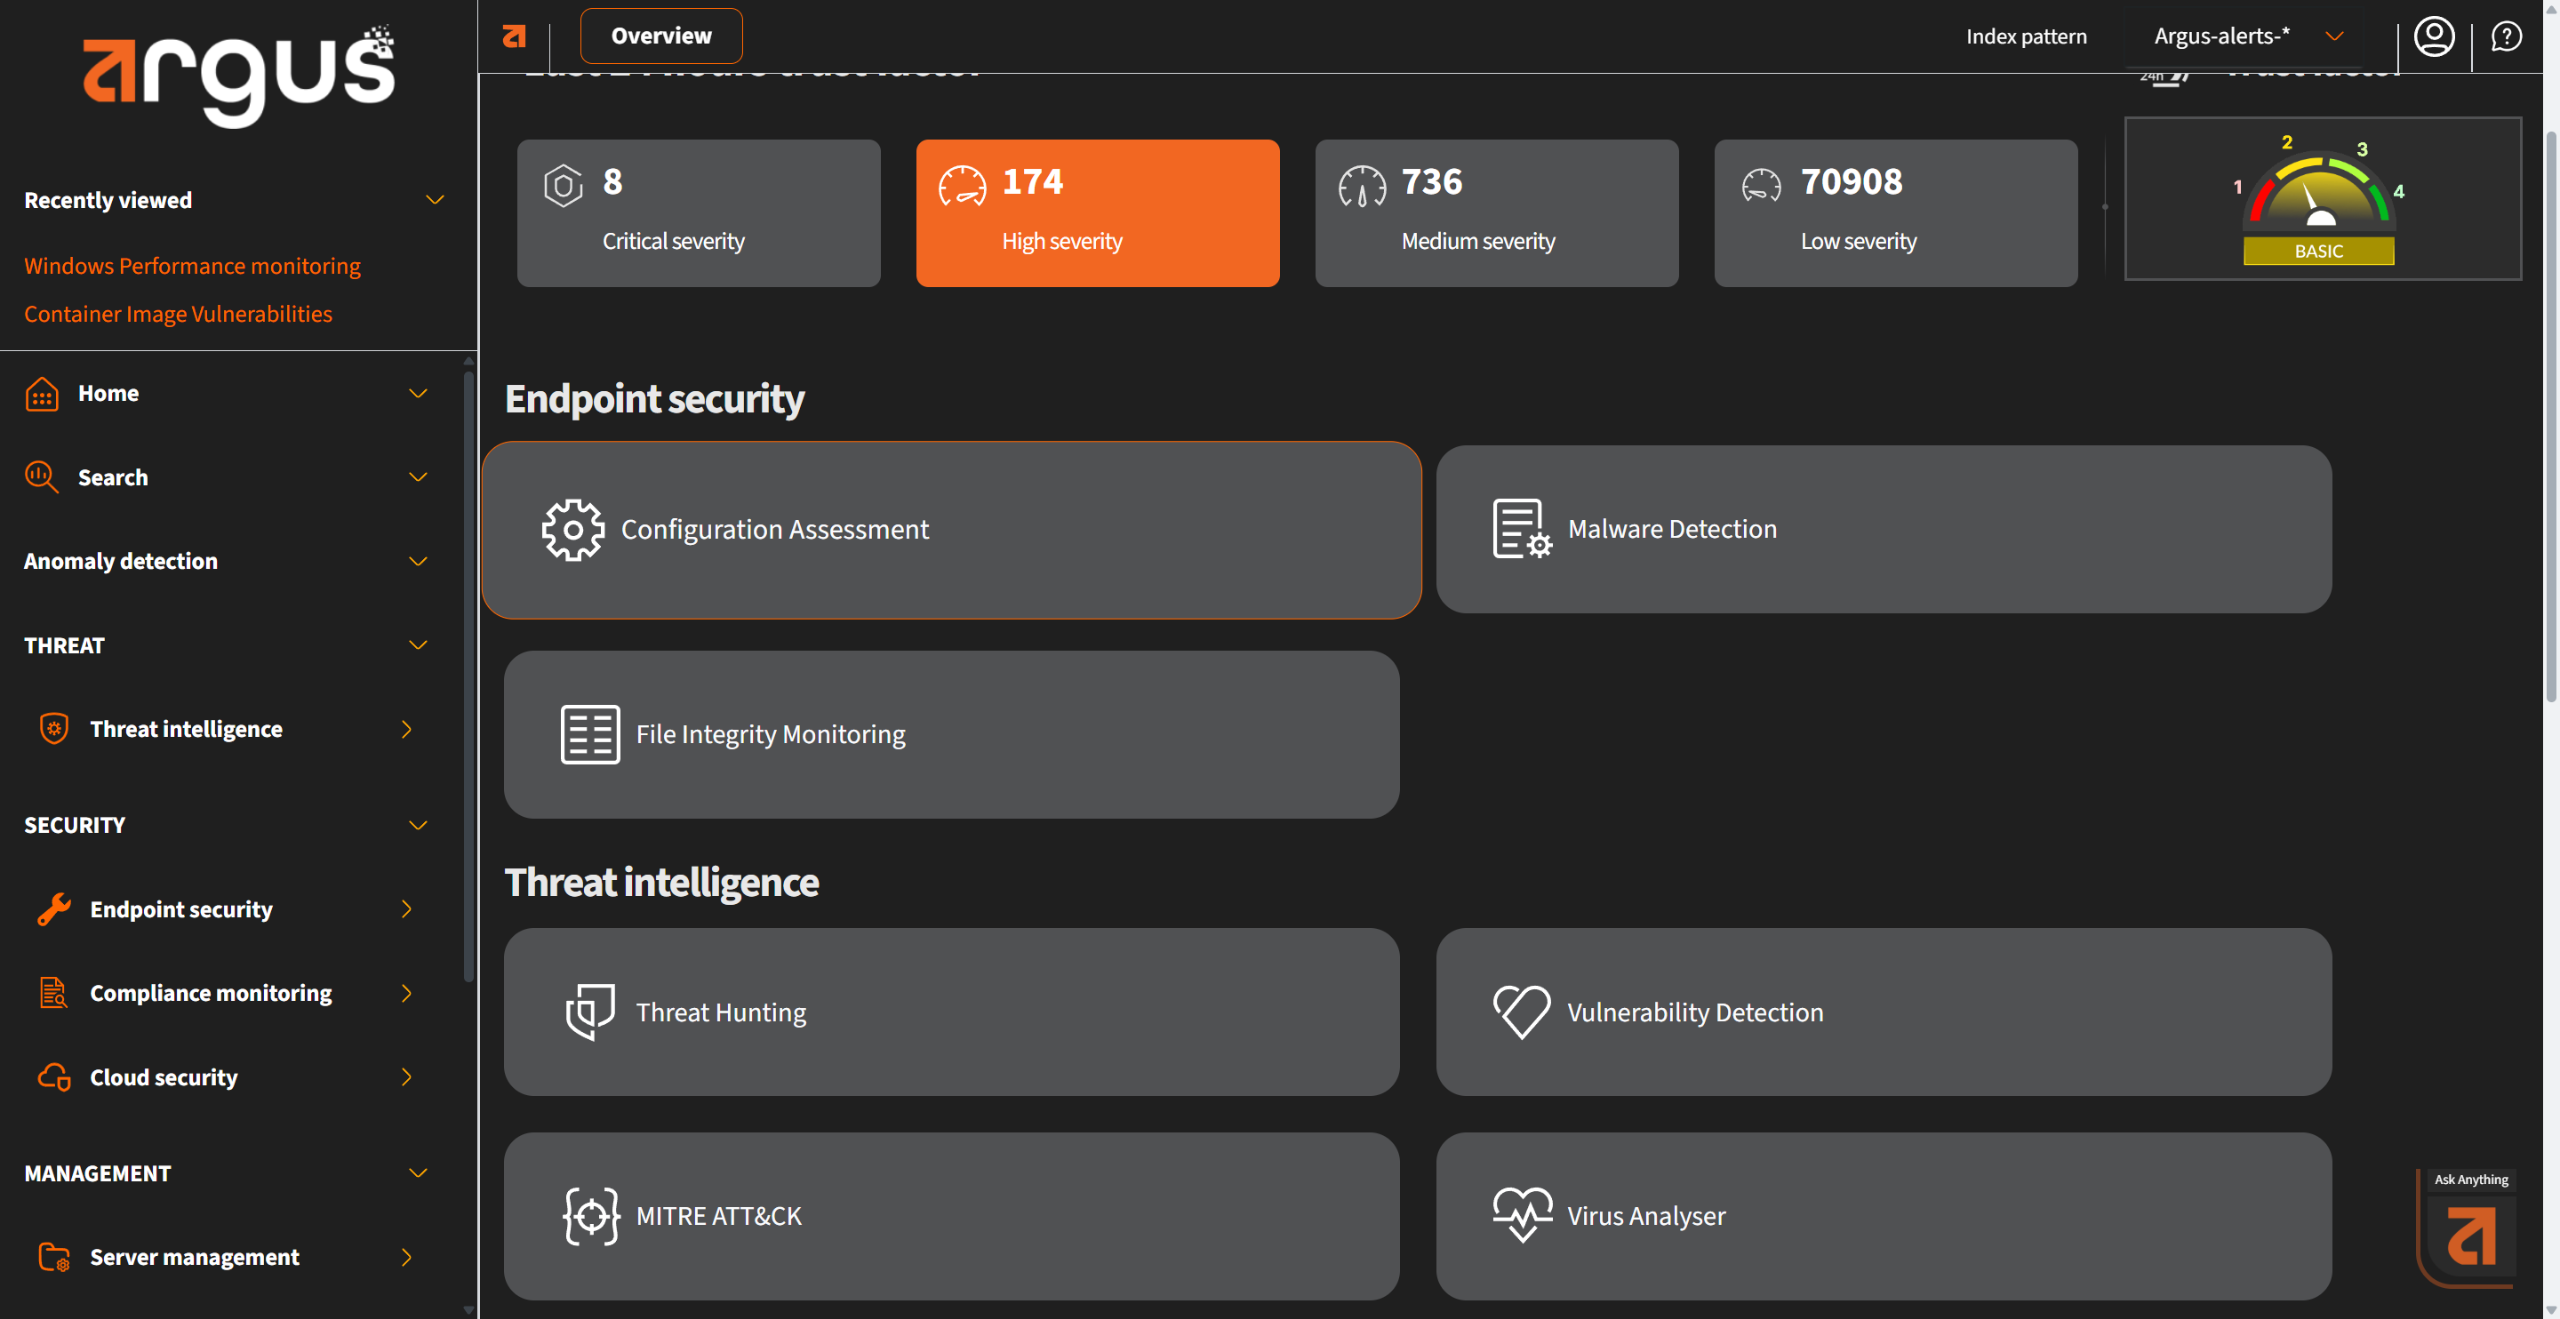
Scalable and Customizable Architecture
Whether you operate in a cloud-first environment or a hybrid model, Argus adapts to your architecture. Its modular design ensures you can scale up as needed and customize your security analytics without technical roadblocks.
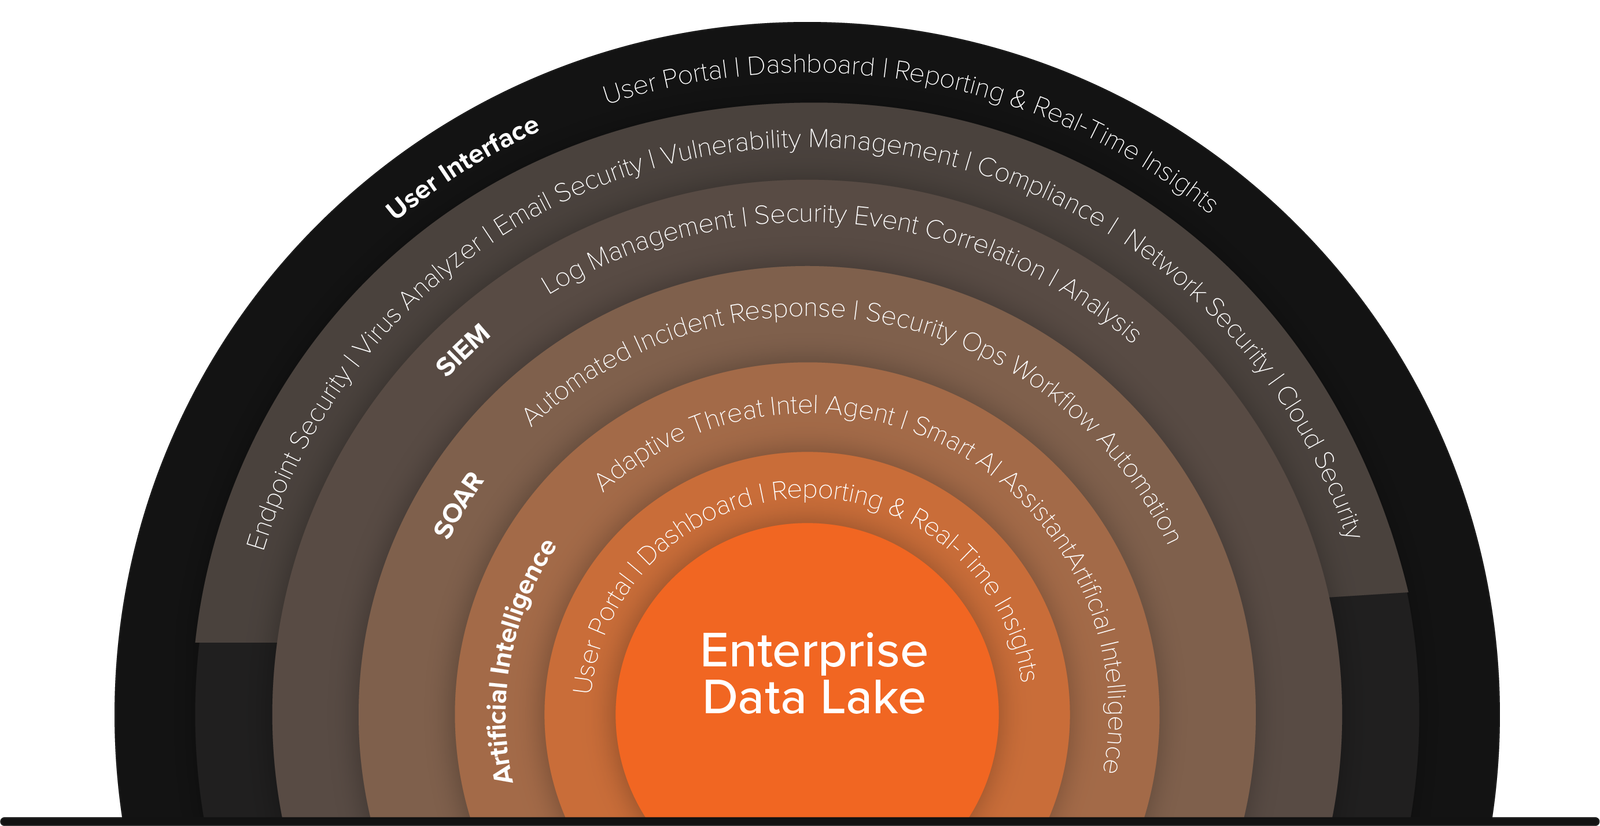
Integration with Splunk, ELK, and More
Already using another SIEM? Argus integrates effortlessly with your existing Splunk or Elastic Stack setup, enhancing your current security workflows with enriched telemetry, context, and intelligent detection.
Threat Intelligence and Contextual Insights
Argus enriches your log data with contextual threat intelligence, helping your analysts understand the bigger picture and take decisive action without delay.
Custom Dashboards and Reports
You can create intuitive dashboards that track key metrics, compliance status, and incident trends. Reports are fully customizable, making it easy to meet internal and regulatory requirements.
Why Argus SIEM
Argus delivers the best of both worlds — a powerful built-in SIEM for teams that want a full solution out of the box, and seamless integration for teams that rely on Splunk, ELK, or other platforms.
See what real-time security looks like with Argus SIEM
Talk to an engineer to see Argus in action. Whether you're upgrading your current SIEM or starting fresh, we're ready to help you get started.
[ Related capabilities ]
[ INTEGRATIONS ]
Third-Party Tool Integrations
Argus connects natively to CrowdStrike, SentinelOne, Microsoft, Okta, and 95+ other tools — orchestrating detection, investigation, and response across them from a single platform.
[ DETECTION ]
Real-Time Threat Detection
Argus analyzes behavior patterns, monitors activity in real time, and provides context-rich alerts to stop threats at the source.
[ EXPOSURE ]
Vulnerability Management
Argus continuously scans your environment, simulates real-world attacks, and guides your team with actionable remediation to eliminate risks before they're exploited.
Ready when you are
See Argus in your environment
Talk to an engineer for a 30-minute working session and see how Argus converges detection, response, and exposure management into a single platform.