Intelligent TDIR + CTEM Platform
For Proactive Cyber Risk Management
Argus combines Threat Detection, Investigation, and Response (TDIR) capabilities with Continuous Threat Exposure Management (CTEM), making it a unique and comprehensive cybersecurity solution.
- No Complex Tool-Suite, No Complicated Integration
- Detects, Identifies, & Prevents Threats Real-Time
- Effortless Out-of-the-box Automation with 96+ Tools
- Agentic IAM for AI Agents & Machine Identities
- Up to 75% Savings on Operational Costs
The cyber-defence iron dome — built by operators.
Argus is a Swiss-army knife for cybersecurity: multiple intercept layers — detection, response, identity, exposure, automation — converged into one platform that watches, decides, and acts in real time.
Multi-layer interception
Concentric defence layers catch threats at the perimeter, the endpoint, and inside identity.
One converged platform
13+ security functions on a shared data and decision layer — no add-ons, no swivel-chairing.
Built by 24×7 SOC operators
Designed by the same people who run it in anger every day. Tuned for signal, not noise.
Best value in cyber. All-in-one. No add-ons.
One flat platform, one price, every capability included — and it works alongside the security tools you already own.
[ All-in-one ]
13+
Security functions converged in one platform. No tiers. No add-ons. Everything included.
[ Plays nicely ]
95+
Tools onboarded out of the box — your CrowdStrike, SentinelOne and SIEM investments stay in play.
[ Best value ]
75%
Lower operational cost vs. running a multi-vendor stack — measured across real customer deployments.
Single Platform Delivering Enterprise-level Visibility and Control
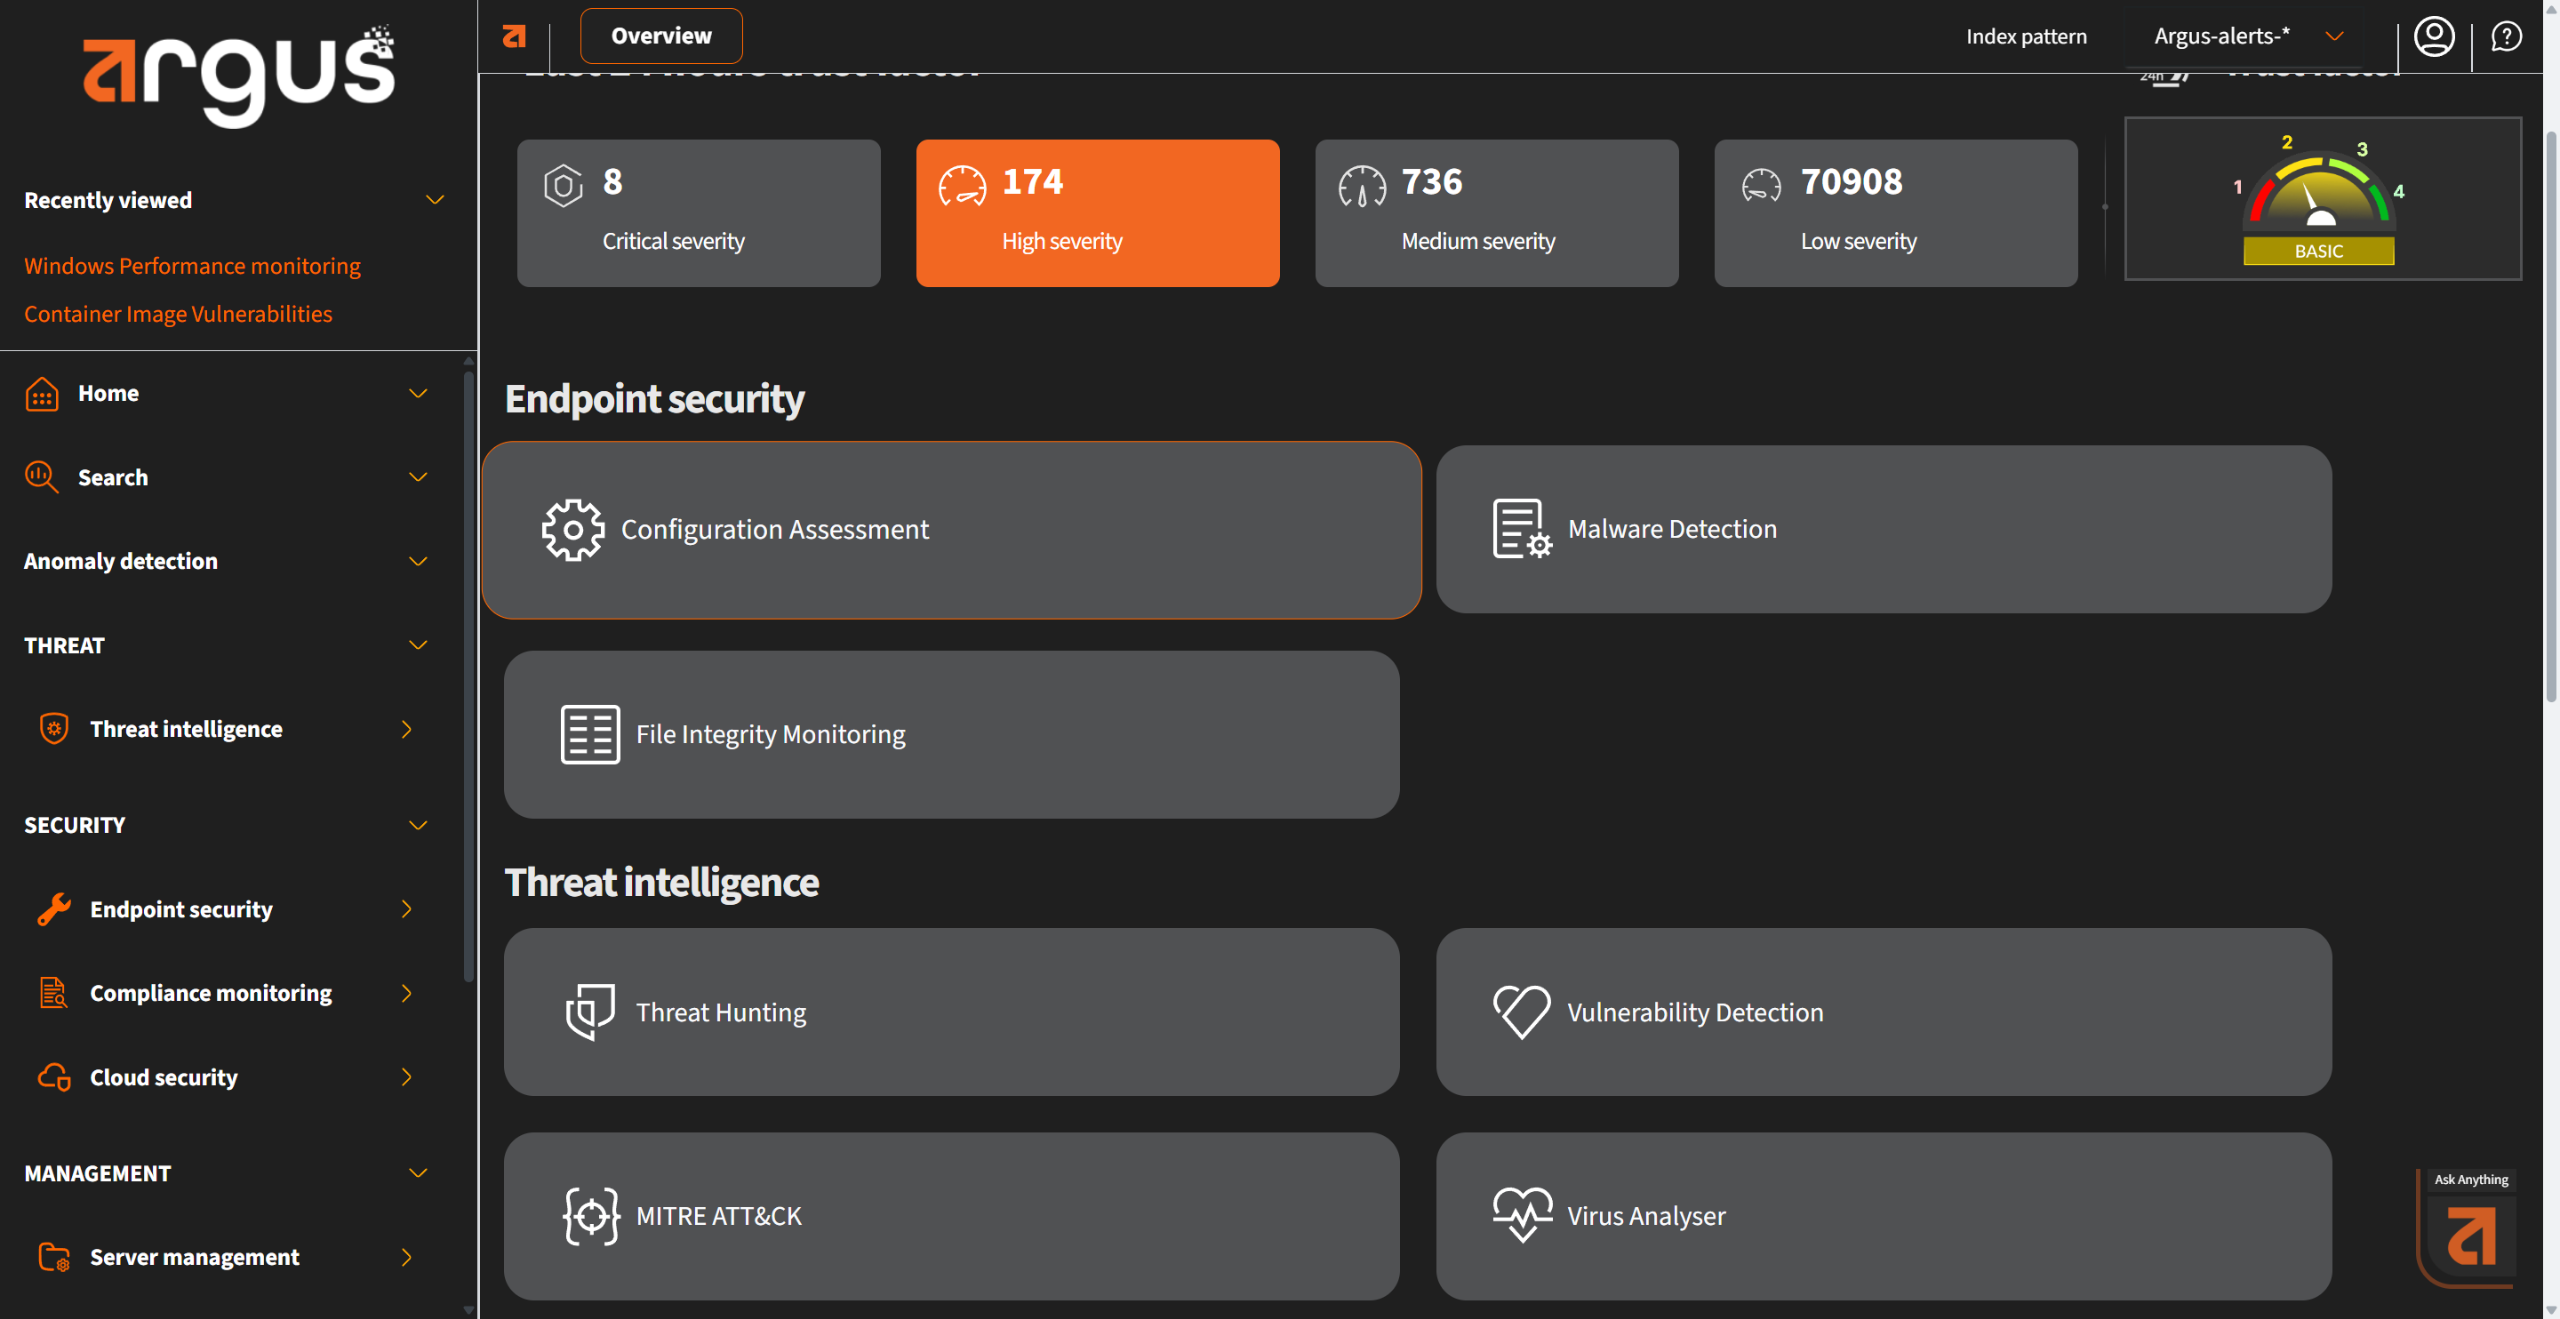
Still navigating multiple tools to contain threats and spot risks? With 13+ built-in core security capabilities, Argus delivers centralized insight and intelligent automation for smooth security operations.
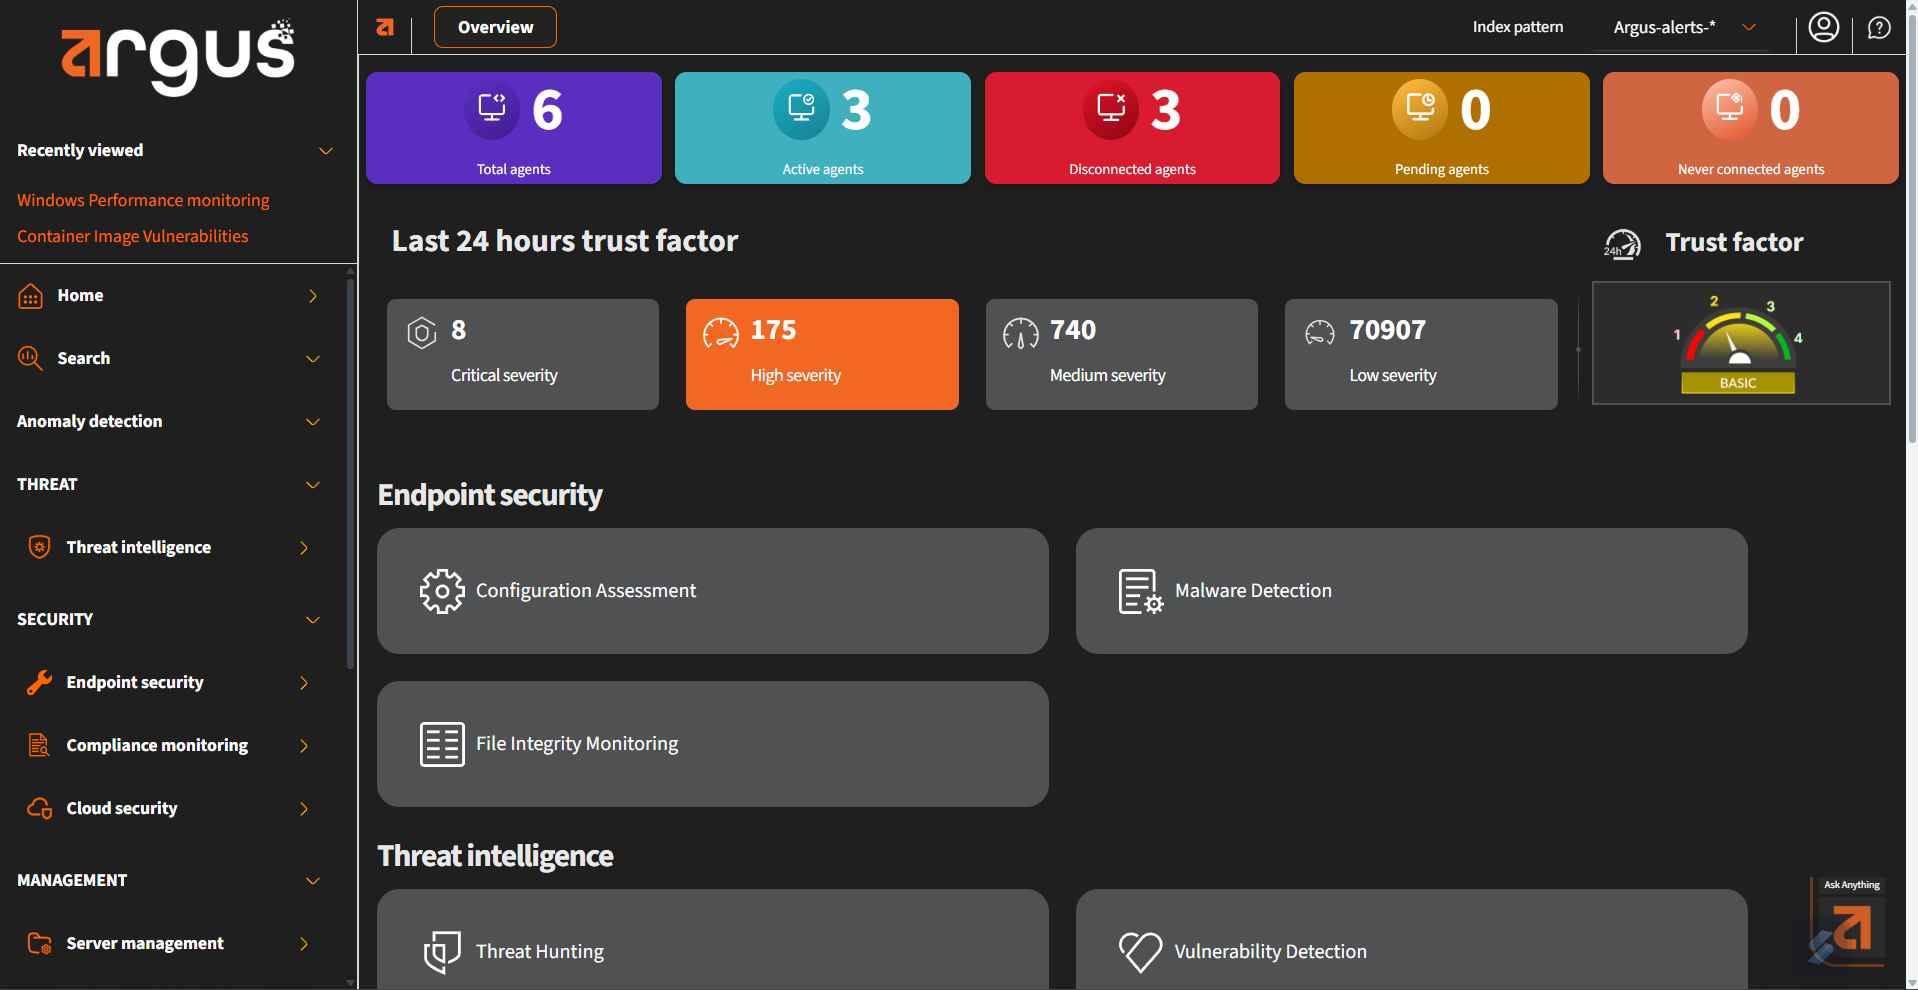
argus.dashboard / threat intelligence
Trust Score
94
+2.1%
Active Threats
3
-12
Coverage
13/13
100%
MTTR
6m
-38%
Top techniques (MITRE ATT&CK)
- T1059Command & Scripting42
- T1486Data Encryption18
- T1110Brute Force11
- T1566Phishing9
See how Argus protects every layer
From detection to response to cloud — one platform, complete visibility.
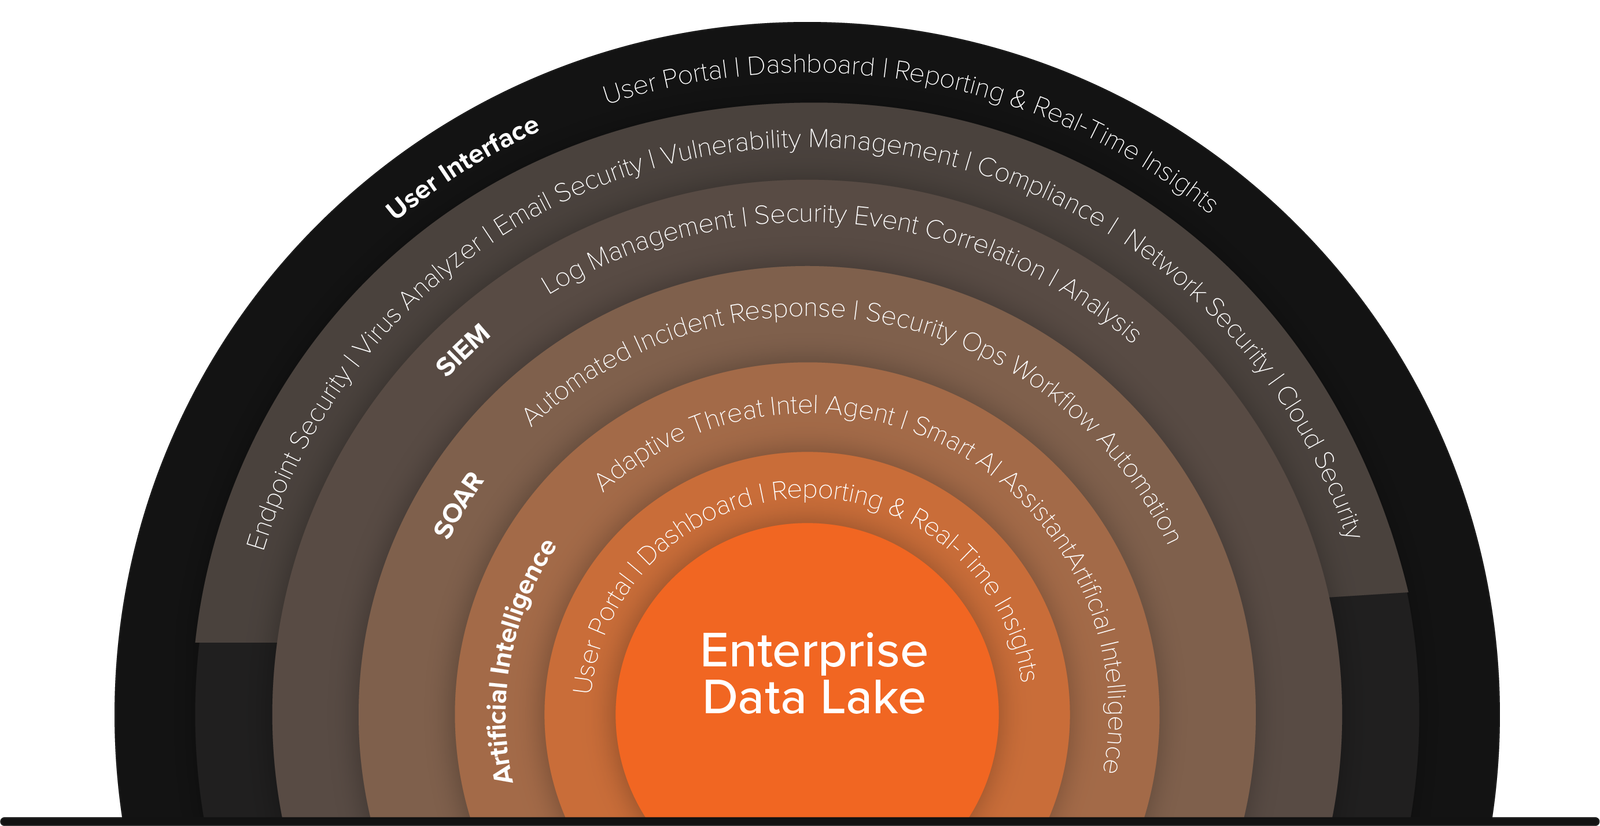
Built-in support to onboard 96+ tools
Argus converges your stack — from endpoint and cloud to identity, network, and threat intel — around a single Enterprise Data Lake. SIEM, SOAR, and AI-driven automation are first-class layers, not bolt-ons.
Detect threats before they escalate
A streaming detection engine evaluates every event against behavioral baselines, MITRE ATT&CK techniques, and curated threat intel — surfacing only the signals that matter.
Context-rich alerts that reduce noise
Argus continuously ingests global threat feeds and matches them against activity in your environment. Each alert includes detailed context about the affected asset, user behavior, timeline, and potential impact.
Welcome to the Argus Dashboard Tour
Join us in this interactive walkthrough as we take a quick look inside the Argus Dashboard and its key capabilities.
A 'Cyber Swiss Army Knife', born from a single idea
At Genix, we envisioned a single tool that doesn't just integrate but converges multiple security functions into one unified defense. From this idea, Argus was born.
Integrates Easily With Existing Setup
Argus adapts to any security environment. It integrates with your current solutions, improving your security posture with real-time threat detection and unified threat intelligence.
Single Reliable Trust Score
Assessing your security posture is no longer a hassle. Argus' Trust Score keeps you informed in real time, enabling quick, informed decisions and keeping you ahead of threats.
Cost Effective
A straightforward pricing model with no extra fees or setup costs. It cuts down on expensive security stacks and eliminates the need for additional resources to maintain them.
Built-in features that work together effortlessly
Integrated solutions rely on separate tools, creating compatibility issues, rising costs, and management challenges. Argus eliminates these issues with built-in features for faster detection, response, remediation, and prevention.
NextGen XDR Engine
Argus collects and correlates data from endpoints, cloud, networks, and identity systems to detect threats in real time, perform root cause analysis, and provide complete situational awareness.
Built-In SIEM and SOAR
High-speed log ingestion, intelligent alert correlation, and automated incident response within a single platform — reducing operational complexity and accelerating threat mitigation.
Agentic IAM / NHI Management
Register, govern, provision, and revoke access for AI agents and machine identities. Least-privilege roles, gateway enforcement, and a full audit trail replace static credentials.
Phishing & Ransomware Defense
Argus identifies spoofing, social engineering, and encryption anomalies to detect phishing and ransomware early, enabling automated containment that minimizes damage and downtime.
Identity management for the AI agent era
AI agents are no longer simple assistants; they execute real actions against real systems. Argus treats every agent, service account, bot, and workload as a first-class identity with governed access, controlled capabilities, and a fully auditable lifecycle.
Register & Classify
Onboard AI agents, service accounts, bots, and workloads as managed non-human identities with owners, metadata, and status.
AI-Generated Roles
Argus generates resource-specific roles and granular entitlements for review and approval — no hand-picked privileges.
Approve & Provision
Requests flow through approval workflows before the provisioning engine creates accounts, assigns roles, and records history.
Gateway Enforcement
Every runtime request passes through the Argus Gateway with policy checks and injection validation before reaching the resource.
Least Privilege by Default
Entitlements are resolved from approved roles, so agents get only the access they need — and nothing more.
Audit & Revoke
Full traceability for every provisioning, policy, and runtime decision, with partial or full revocation when access changes.
Built-in support to onboard 96+ tools
Argus converges your stack — from endpoint and cloud to identity, network, and threat intel — around a single Enterprise Data Lake. SIEM, SOAR, and AI-driven automation are first-class layers, not bolt-ons.
Explore the platformThe Swiss Army Knife approach to cybersecurity
Argus brings together 13+ core security functions in one platform, delivering advanced Extended Detection and Response (XDR). With inbuilt SIEM and SOAR, it ensures accelerated security effectiveness and real-time protection.
Download WhitepaperLatest from our blog
Blog · March 18, 2026
The Hidden RAT: Detecting PureHVNC with Argus by Genix Cyber
by Soundarya Kale
Blog · March 3, 2026
LockBit 5.0: Anatomy of a Modern Ransomware Operation
by Soundarya Kale
Blog · February 17, 2026
OpenClaw: What Security Teams Need to Know About "The Lobster"
by Soundarya Kale
Trusted by security teams worldwide
"The Argus platform is very flexible and inexpensive, which is what the market needs."
VP
Internal Security Provider
"This Tool is like a Swiss Army Knife. It is a Cybersecurity Swiss Army Knife."
Senior Director
Leading Global IT Products and Network Solutions Provider
"Argus is too good to be true and looks to solve all our problems."
CTO
Public Sector Multi-National MSP
Ready when you are
See Argus in your environment
Talk to an engineer for a 30-minute working session and see how Argus converges detection, response, and exposure management into a single platform.